If you give AI full access, isolate the entire PC
AI agents and Codex can work faster when given more freedom.
But on a main PC, that freedom can expose credentials, cloud-synced files, personal data, and company information.
To let AI work freely, first isolate its environment.
Before crafting a powerful prompt, start AI experiments in an isolated environment where things can break safely.
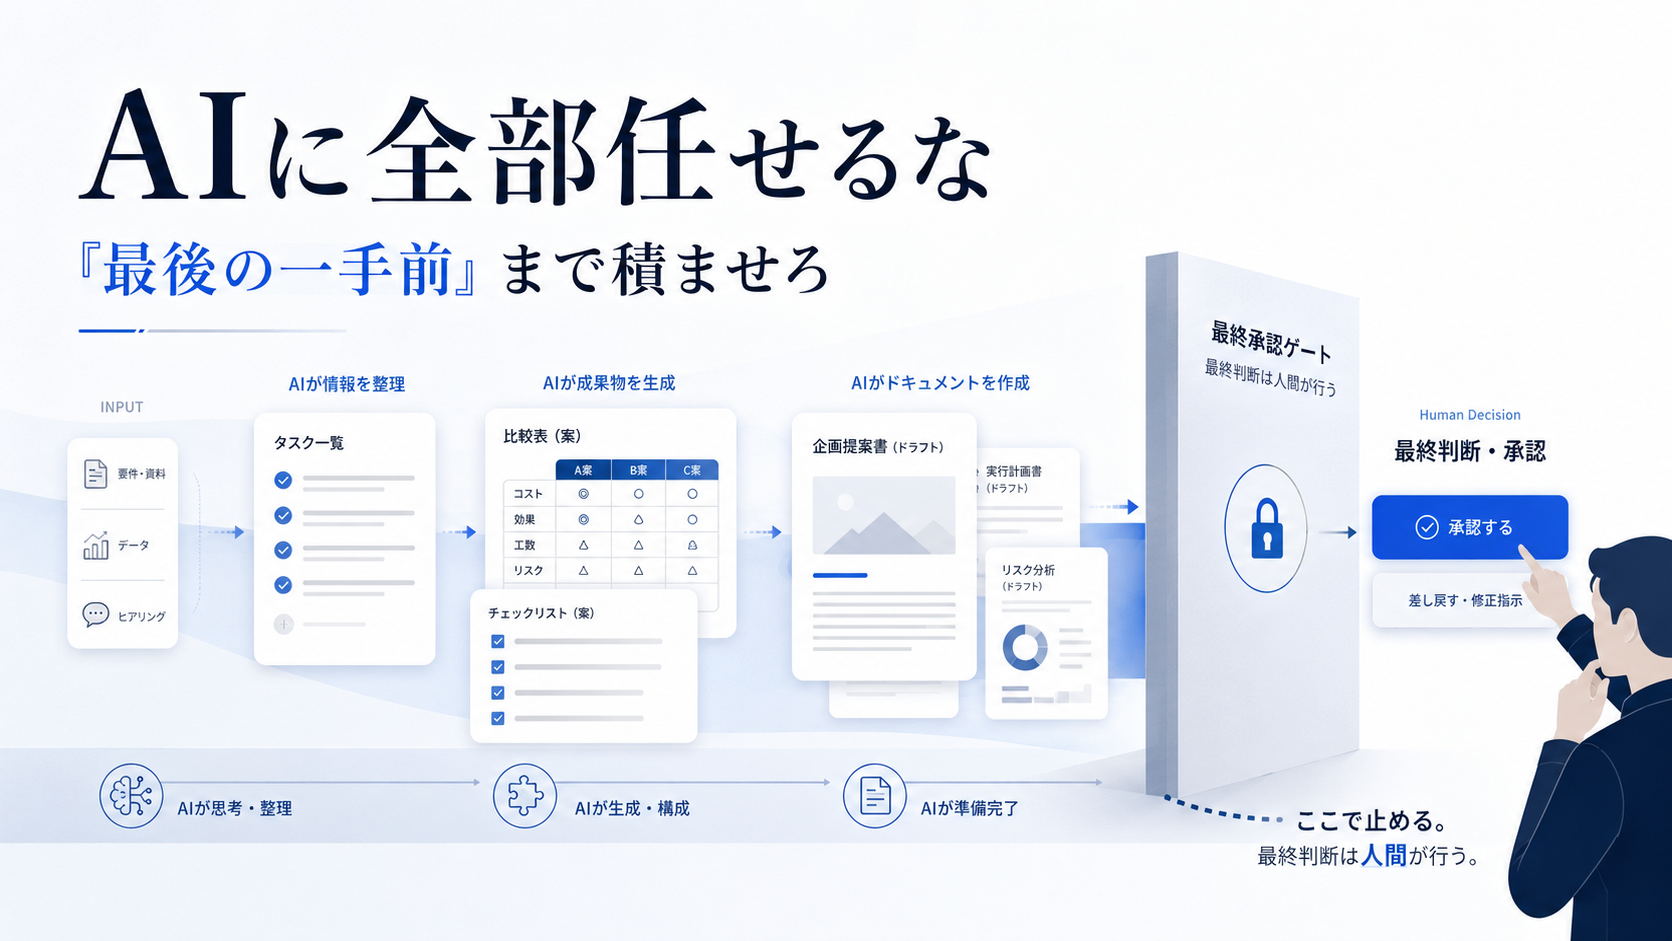
The biggest risk in AI experimentation is where it runs, not the AI itself
When Codex or an AI agent works for a long time, it may try to access a much wider range of things than you expect.
It may search for files, inspect settings, open a browser, install tools, review logs, read environment variables, create work folders, and visit external sites.
This can be fascinating to experiment with: AI can research, implement, verify, and write a report without requiring a person to handle every detail.
But doing this on your main PC quickly becomes risky. Work files, personal information, logged-in browser sessions, cloud sync, API keys, old development environments, email, and payment accounts may all be within reach.
Before giving AI freedom, first create a place where it is safe to work freely.
A clean install is faster than trying to sanitize an existing PC
When repurposing an existing PC for AI experiments, it may seem that deleting unnecessary files is enough.
But many things can remain hidden: environment variables, PowerShell history, Docker settings, cloud SDKs, browser profiles, authentication tokens, SSH keys, service-account keys, old downloads, and synced folders.
You can search for and delete these one by one, but it is easy to miss something. AI audits can also report false positives; deleting every file that looks suspicious is not a good solution either.
That is why a clean install is safer than cleaning up an existing setup when preparing a PC for unrestricted AI experiments.
Start from a clean slate and install only what is essential: a browser, an editor, a sandbox folder, and a recovery process. Set it up from the beginning as a PC with no important data on it.
This makes decisions simpler. The less there is to protect in an environment, the easier it is to give AI room to work.
Do not use OneDrive or the desktop as a workspace
Cloud sync deserves special attention on a PC used for AI experiments.
OneDrive, Google Drive, Dropbox, browser sync, and desktop sync are convenient in daily use, but they can move data unintentionally when AI has broad freedom to work.
For example, a folder that appears to be on the desktop may actually be inside OneDrive and sync automatically. Generated logs, test files, downloaded assets, and work notes could be uploaded to the cloud.
That may be fine for instructions or files intended for publication. It is risky if personal data, company information, API keys, credentials, or unreviewed experiment logs are mixed in.
Keep AI's workspace outside cloud sync. For example, use C:\Lab or C:\Codex_Workspace as a clearly defined workspace.
Restrict AI's workspace to one of these folders. Do not use the desktop, Documents, Downloads, or a OneDrive folder as its regular workspace.
If you give AI freedom,
First isolate the PC so AI can work freely there.
Deleting API keys and service-account keys locally is not enough
API keys and other credentials are among the most sensitive things to find on an AI sandbox PC.
OPENAI_API_KEY, HF_TOKEN, Google Cloud service-account keys, SSH keys, and Docker login credentials all create risk if they remain on the PC, even if AI never uses them directly.
The important thing is not to assume that local deletion makes them safe.
If an AI agent or work process might have seen a key, revoke and replace it in the service first. Then remove it from the PC.
Environment variables also have different scopes. Removing a value from User or Machine may leave it in the Process environment of a running PowerShell or Codex session.
So a variable may still appear to be present until you restart, even after you think you have removed it.
Verify secrets by checking whether they were revoked at the service and whether they remain after a restart—not just whether a file was deleted.
The environment design can greatly change the risks of the same autonomous AI
Where AI runs matters as much as what it does. The same task has different implications on a main PC and on an isolated machine.
- Run AI experiments on the main PC
- Use a folder under OneDrive as the workspace
- Leave browser sessions signed in
- Keep API keys and SSH keys on the machine
- Keep company and personal data on the same device
- Experiment without a recovery plan
- Experiment on a reset, secondary PC
- Limit the workspace to a folder outside sync services
- Disable browser sync and automatic sign-in
- Revoke and delete secrets, then check again after restart
- Assume no important data belongs on the machine
- Prepare a USB recovery option first
A safer order for setting up a dedicated PC for Codex
What to check before using a PC for AI experiments
Check at least the following before granting AI broad permissions.
Acceptable environment
- No important data is stored on it
- No company files are on it
- Cloud sync is disabled
- No API keys or SSH keys remain
- The workspace is outside synced folders
- A recovery USB or reinstall option is ready
Mistakes to avoid
- Start an unrestricted experiment on your main PC
- Use the desktop as the workspace
- Leave the browser signed in
- Delete important files carelessly based on an audit result
- Delete a key locally without revoking it
- Change OS settings without a recovery option